Developer Productivity
GitHub Copilot Governance Before You Scale Licenses
Buying GitHub Copilot seats is easy. Scaling them across an engineering organization without leaking secrets, skipping review, or creating un-auditable agent output is not. This note covers the governance work we run before license counts grow.
Parveen KR3 min read
Licenses are not an adoption program
Most enterprises start Copilot as a procurement event: a SKU, a security questionnaire, and a pilot team that already wanted the tool. Ninety days later, usage is uneven, security still cannot answer which repositories are in scope, and platform owners have no metric except “seats assigned.”
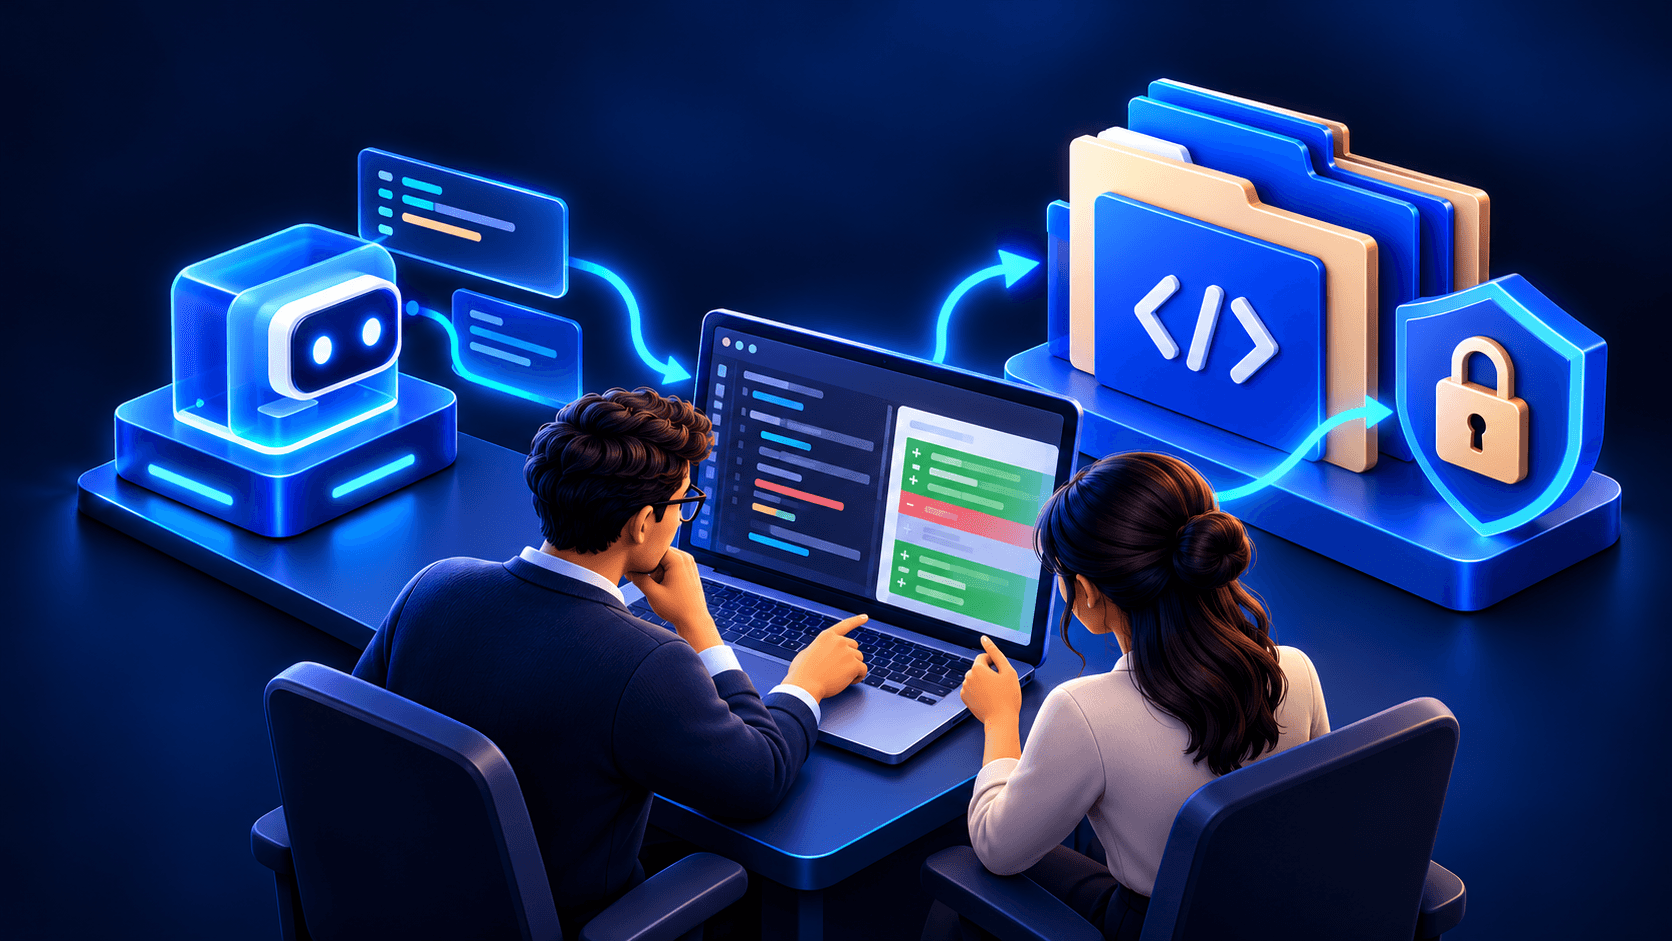
The teams that get value treat Copilot as an operating-model change. That means a named owner, a written repository allow-list, content exclusions for secrets and regulated paths, and a human-review rule that applies even when the agent wrote most of the diff.
Four controls that should exist before wave two
Identity and access. Copilot should follow the same Entra groups and joiner-mover-leaver process as other engineering tools. Shared seats and unmanaged personal accounts are how policy dies quietly.
Content exclusions. Exclude credential stores, infrastructure secrets, customer data extracts, and any path legal has already flagged. If exclusions are “we will add them later,” later never comes.
Content exclusion is not a universal data-protection boundary. GitHub’s documentation says support depends on the Copilot surface and the mode in use. Information from an excluded file can still reach Copilot when the editor supplies it indirectly, such as type details or project settings. Exclusions also do not apply to symbolic links or to repositories on a remote filesystem. A repository instructions file guides the assistant. It does not enforce who can read the repository.
Repository instructions. A short AGENTS or Copilot instructions file per critical repo beats a 40-page standard nobody opens. Spell out language, test commands, and what the agent must not touch.
Human review. Agent-authored pull requests still need a reviewer who can explain the change. “The model wrote it” is not an audit trail.
MCP and multi-tool reality
Many engineering orgs will not stay on GitHub Copilot alone. Cursor, Claude Code, and Codex show up in the same quarter. If your policy only names one vendor, developers will route around it.
We treat MCP servers, repository access, and secret injection as a single control plane: approved servers, denied local filesystem sprawl, and logging that security can actually read. The goal is not to ban tools. It is to make the next tool inherit the same boundaries.
What a 30-day governed pilot looks like
Week one: inventory current coding-agent use, pick two repositories, write exclusions and instructions, agree success metrics (review time, escaped defects, secret-scan hits — not “lines accepted”).
Weeks two and three: run the cohort with office hours, measure those metrics, and capture exceptions.
Week four: decide scale, pause, or redesign. Only then buy the next block of seats.
If you need a starting program, the VNode AIC-220 Secure AI Coding and Governance track and the GitHub Copilot platform page are built around this sequence — not a feature tour.
References
- GitHub Copilot
- Developer AI
- Governance
- MCP
- Agentic Software Engineering
Next step
Want this workflow reviewed against your own work?
A consultant looks at the business outcome, the data, and who has to approve the action before recommending a scope.
